When a serious cyber incident hits, the clock starts running. Under NIS2, covered companies have to report significant incidents to their national authority in three steps, with firm deadlines. The rules are in Article 23 of the directive, and they are one of the parts people most often get wrong, simply because nobody looked at them before the day it happened.
This article explains the three deadlines in plain language and shows how to prepare so that reporting is a routine task, not a panic.
What is a "significant" incident?
Not every problem has to be reported. NIS2 asks you to report incidents that are significant. An incident is significant when it:
- has caused, or could cause, severe disruption of your services or financial loss for your company, or
- has affected, or could affect, other people or organizations by causing considerable material or non-material damage.
For digital providers (such as cloud, data center, managed service and online marketplace providers), an EU implementing regulation, Regulation (EU) 2024/2690, adds concrete thresholds. For everyone else, your national law and your authority's guidance fill in the details.
A practical rule: if you are unsure whether an incident is significant, prepare the early warning anyway. It is much easier to decide not to send it than to write it from scratch at hour 23.
The three deadlines
The deadlines count from the moment you become aware of the significant incident.
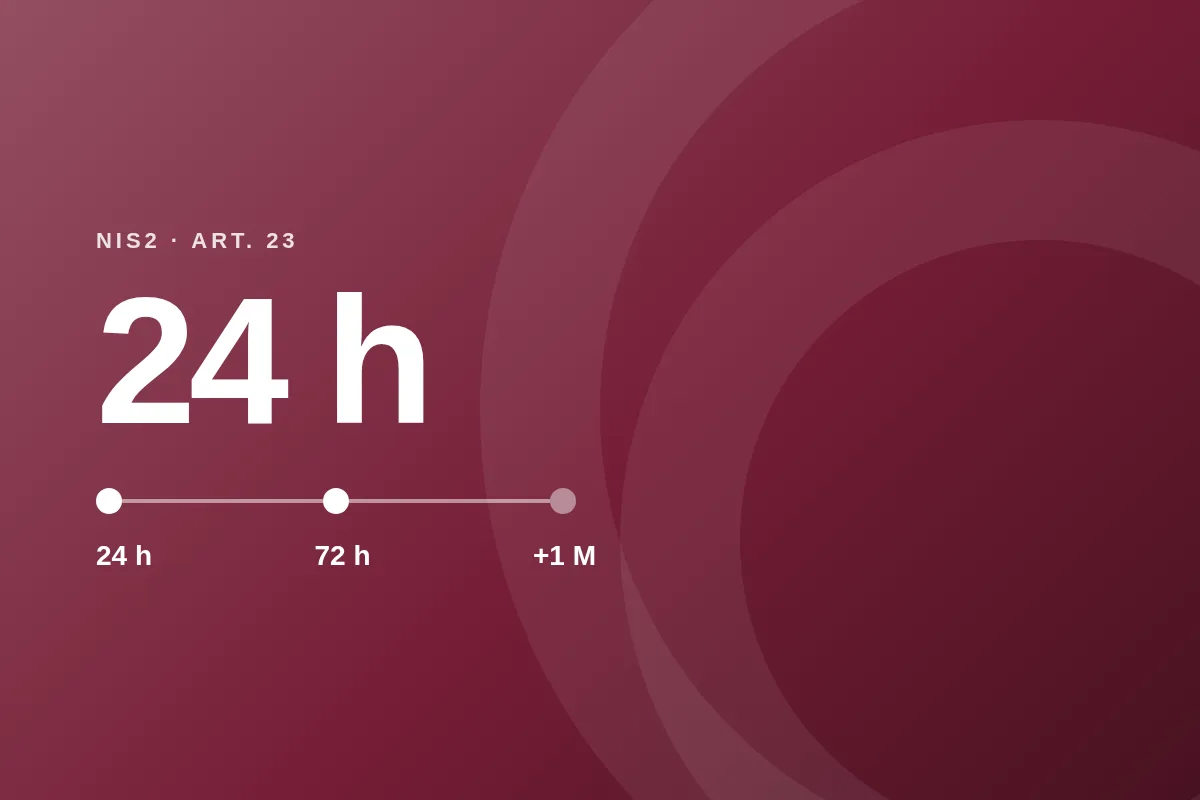
- Early warning within 24 hours. A short first message to your CSIRT or competent authority. It says that a significant incident happened and, where possible, whether you suspect it was caused by an unlawful or malicious act, and whether it could have an impact in other countries.
- Incident notification within 72 hours. An update of the early warning with an initial assessment: how severe the incident is, what impact it has, and indicators of compromise where available.
- Final report within one month. One month after the incident notification, a detailed report: a description of the incident and its severity and impact, the type of threat or root cause, the measures taken and ongoing, and any cross-border impact.
If the incident is still ongoing after one month, you send a progress report instead, and the final report within one month after you have handled the incident. The authority can also ask for intermediate reports at any time.
Where it makes sense, you also have to inform the recipients of your services that could be affected, and tell them what they can do to protect themselves.
Personal data: GDPR has its own clock
If personal data is involved, the GDPR applies in parallel. A personal data breach has to be reported to your data protection authority within 72 hours, unless it is unlikely to create a risk for the people concerned. These are two separate reports to two different authorities, and one does not replace the other.
How to be ready before it happens
Most of the stress comes from searching for information under pressure. A few things prepared in advance make the difference:
- Know who reports. Name the person who decides whether an incident is significant, and a deputy for holidays and weekends.
- Know where to report. Write down your national CSIRT or authority, its reporting channel and any login you need.
- Keep one incident record. Note when you became aware, what happened, which systems and customers are affected and what you did. The reports are built from this record.
- Practise once. Walk through a short exercise: a ransomware case on a Friday evening. Who is called, who decides, who writes the early warning?
How CloudSignLab helps
In CloudSignLab, every incident in the incident register has the NIS2 reporting clock built in. As soon as you mark an incident as NIS2-relevant and enter when you became aware of it, the deadlines for the early warning, the notification and the final report are calculated and shown. Reminders go out before each deadline, and the GDPR 72-hour hint appears when personal data is involved. The record you keep during the incident becomes the basis for your reports, and everything is kept as evidence afterwards.
Start freeThis article is a general introduction, not legal advice. The national law of your country and your authority's guidance decide the details; when in doubt, ask your authority or a legal adviser.